Sécurité
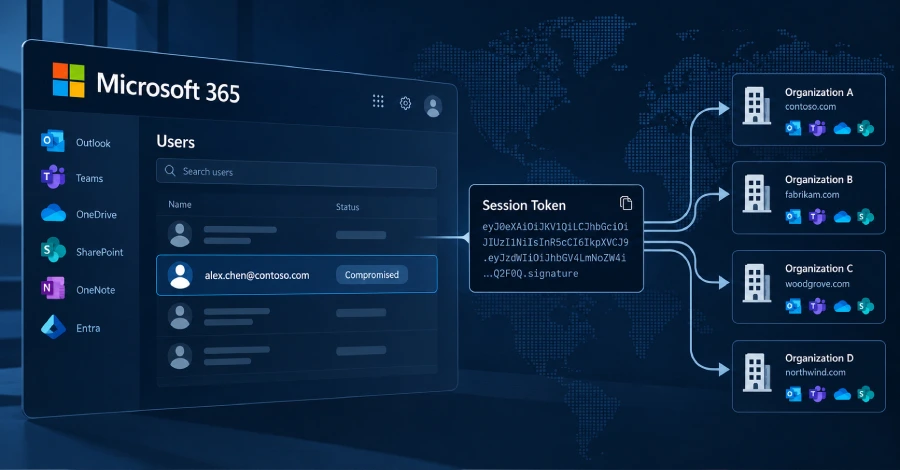
Microsoft 365 Token-Replay Campaign Compromised 97 Accounts at 79 Organizations
Security firm Huntress disclosed a months-long campaign that stole Microsoft 365 sign-in tokens through adversary-in-the-middle phishing, replayed them within minutes to bypass MFA, and then rewrote inbox rules to hide payroll and bonus emails.
The Hacker News
phishingsecurity